Indicators of Compromise vs Behavioral Detection for Web Threat Hunting
Behavioral detection catches novel attacks; IoCs confirm known threats and scope their reach.
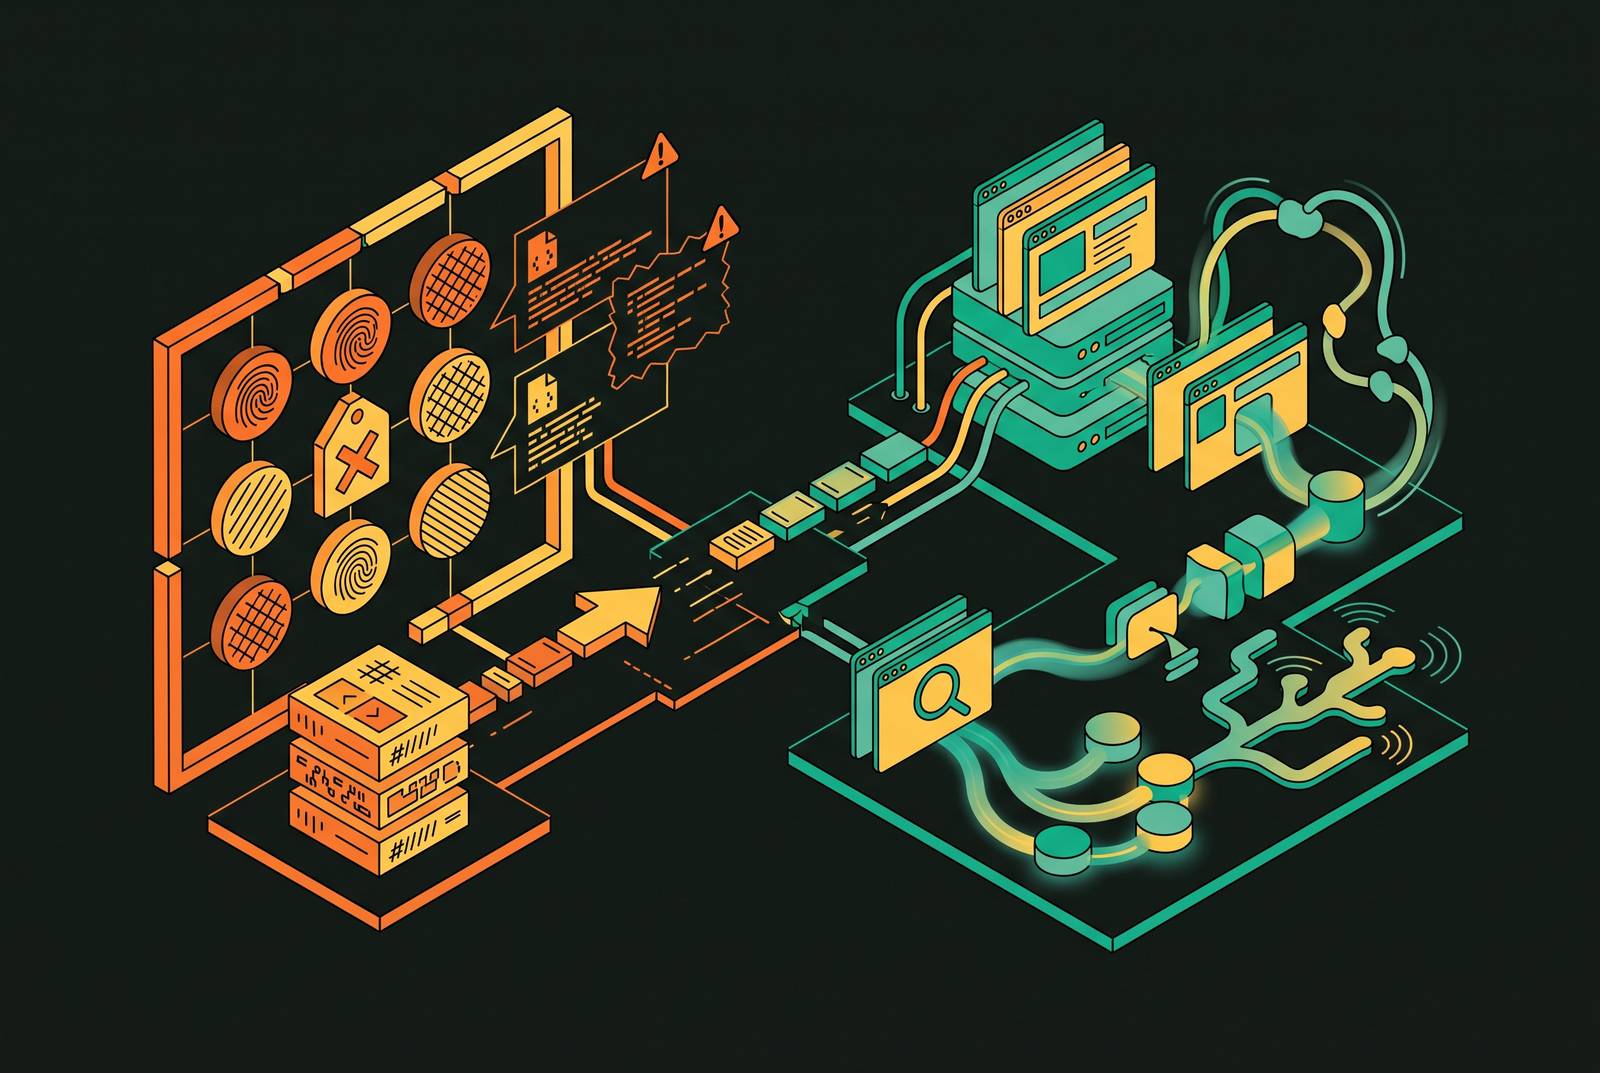
IoCs find known malicious artifacts, while behavioral detection looks at what systems and identities are doing. Effective hunting uses both, drawing on behavior to find attacks that have no known markers and on IoCs to confirm threats and trace their reach once those markers exist.
Why IoCs and behavioral detection operate at different points in the attack timeline
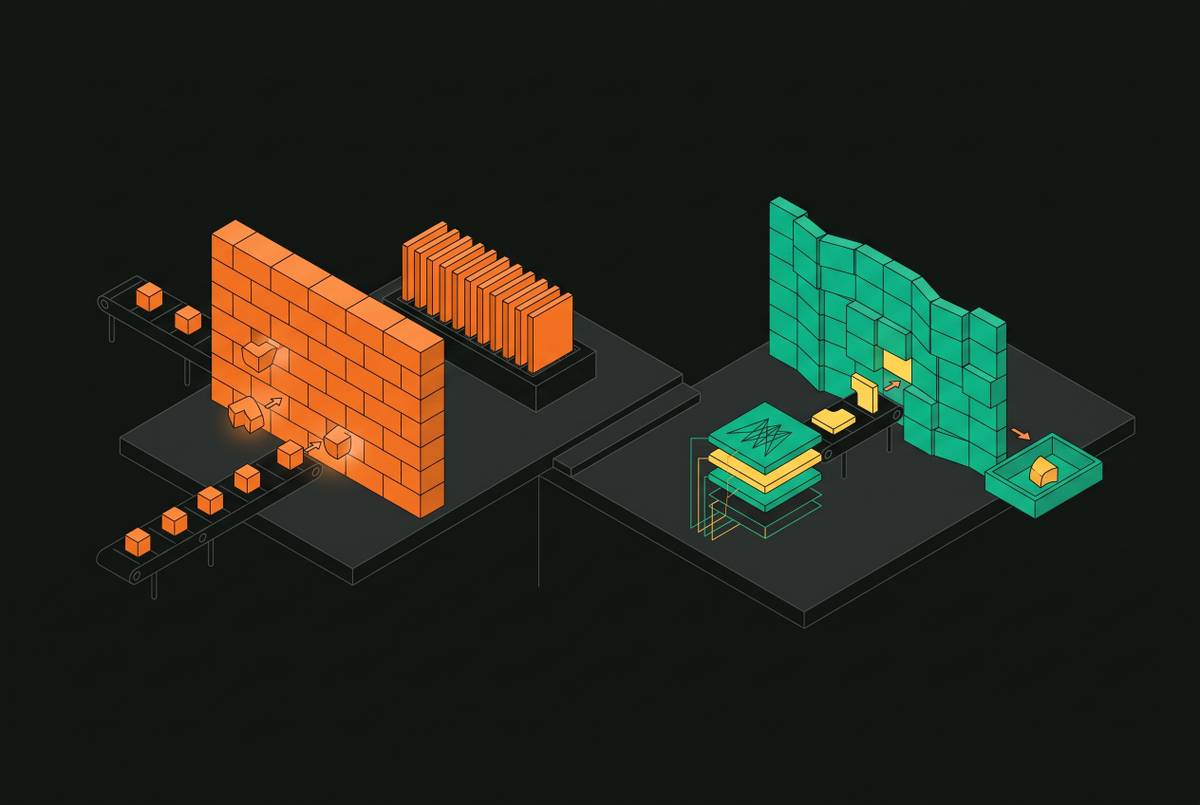
Is this artifact known to be malicious? A match connects something in an environment to prior threat intelligence, whether that something is a file hash, IP address, domain name, registry key change, file path, or email or URL artifact. Its value comes from that prior knowledge. It can turn suspicion into verifiable evidence quickly enough to support scoping and containment.
Behavioral detection starts with a different question. Are these actions proportionate and appropriate for the task? It focuses on Tactics, Techniques, and Procedures, or TTPs, which describe how an attack works. That distinction allows it to catch activity before a file or destination has been attributed to a threat. It also makes living-off-the-land attacks visible when each individual tool call is legitimate but the sequence is not.
The Pyramid of Pain shows why these methods sit at different levels. Hashes, IP addresses, and domains sit at its lower levels because they are easy to detect but cheap for attackers to replace. TTPs sit at the apex because they are harder to detect and more costly to change. Saha et al., in their ASIA CCS’26 study, describe behavioral characteristics as thought to remain stable over time and impose higher costs on adversaries who change them. The practical distinction is between recognizing a replaceable marker and recognizing the method behind it.
What makes IoC-based hunting reliable and where it breaks down
IoC matching is fast, automatable, and suited to searching across many log sources. Hunters can apply it across SIEM, EDR, DNS, proxy, email, cloud, and identity logs to test whether a known threat has touched an environment. Correlating those hits with time windows reveals first-seen and last-seen activity and its spread, helping analysts distinguish noise from compromise.
That strength depends on the quality of the indicator. An exact match to a specific hash or domain is not equivalent to a contextual match involving a filename or an IP range shared with legitimate services. Indicators also need normalization so they resolve consistently across log sources. Without normalization, a search can look exact even as it compares data in different forms. A lone weak match should not trigger the same response as a corroborated chain of compromise.
Time creates another limit on indicator reliability. IoCs are retrospective, and attackers can rotate infrastructure while obsolete indicators remain on detection lists. Legitimate services, infrastructure that is used only briefly, and stolen credentials leave fewer markers that last. Teams should retire stale indicators quickly and treat low-confidence artifacts as hunt hypotheses. Validated, high-value indicators can instead move into blocklists or detection rules.
Saha et al. found that only 34% of threat groups in MITRE ATT&CK have group-specific techniques. Common techniques, including spearphishing, registry-key persistence, and abuse of penetration-testing tools, provide little basis for distinguishing groups. An IoC associated with a named group therefore need not uniquely identify that group’s activity. For hunters, the next step after a confirmed hit is a pivot into parent-child process chains, authentication events, API calls, and data transfers.
What behavioral detection covers that IoCs structurally cannot
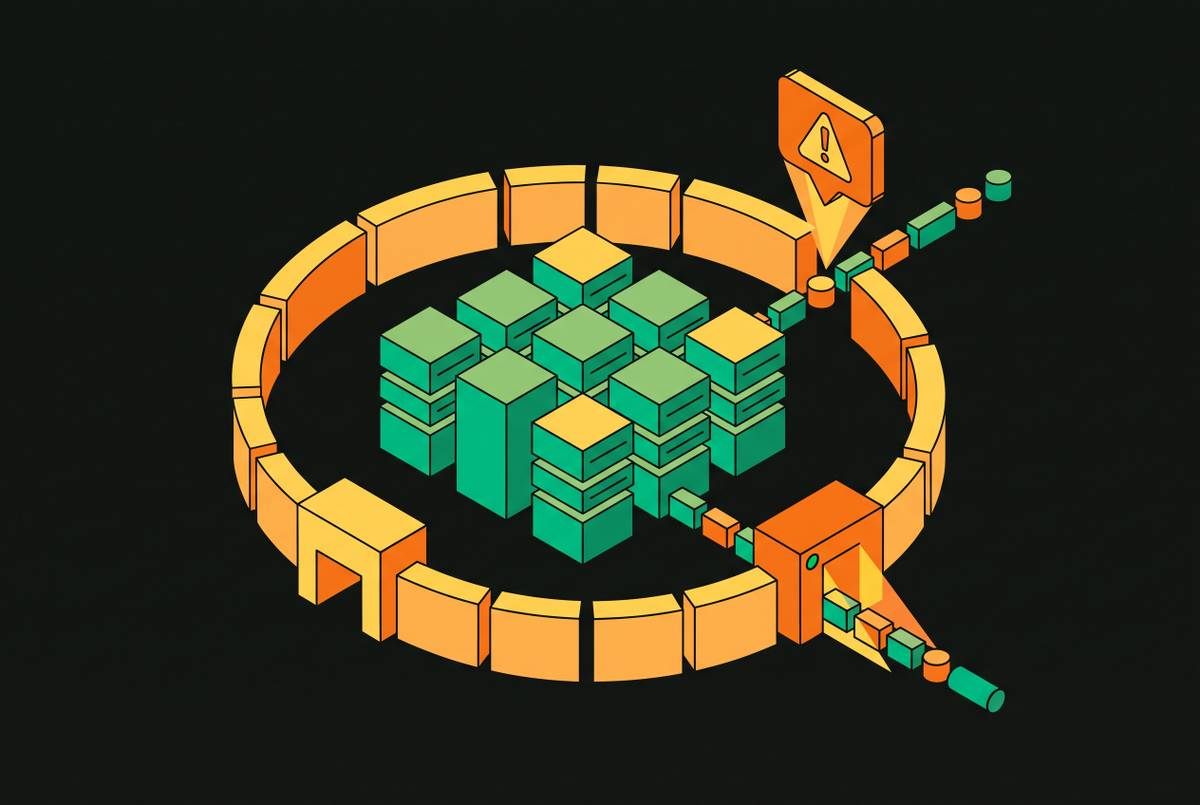
That surrounding context becomes essential when an attack contains no known malicious artifact. An intruder can chain trusted administrative tools, valid credentials, and approved programs into a harmful workflow without supplying a hash or IP address that an IoC search will recognize. The components can all pass an artifact check. Detection then depends on whether their use fits the task, including the order of tool calls, process genealogy, authentication patterns, and the volume of data moved.
The unit of analysis is the connected activity. Instead of looking up each artifact separately, behavioral detection correlates actions across the attack chain and weighs their combined significance. Trellix SecondSight evaluates low-confidence alerts, anomalous behaviors, infrastructure reuse, and identity abuse together, weighting them by relevance, credibility, and potential impact. Signals that fall below a threshold individually can collectively expose an early-stage intrusion. A clean tool is not a character reference.
Behavioral rules also have a durability advantage because attackers must change their methods. Durability, however, does not make every technique distinctive. The same study found that 73% of ATT&CK groups use group-specific software, making software more discriminating than techniques alone. Exploited vulnerabilities add further signal when combined with those observations.
The cost is ambiguity and the analyst work it creates. An unusual action is not necessarily a malicious one, and behavioral detection must separate meaningful deviations from legitimate work. That makes corroboration central to its usefulness. The Axios npm supply chain attack gives a concrete example of the handoff, with behavioral evidence exposing suspicious execution and IoCs narrowing the search once the malicious infrastructure became known.
How the Axios npm supply chain attack shows IoC and behavioral signals working in sequence
The Axios npm supply chain attack added a dependency on a malicious package that had just been created, plain-crypto-js. That package contained a dropper that fetched platform-specific second-stage payloads from an external command-and-control server, then deleted itself to reduce its forensic footprint. The installation artifact was only part of the evidence. Understanding the compromise also required reconstructing what the package executed and where that execution led.
Behavioral signals provided the early opening before IoC attribution was complete. Unexpected outbound connections from package execution environments, payload fetching from new external hosts, and self-deletion sequences gave detection rules activity to examine. A hash lookup alone could not describe the dropper’s fetch-and-delete sequence, even though a known hash could later help identify the package involved.
Once the infrastructure was known, the investigation gained searchable anchors. Known package hashes, the plain-crypto-js dependency, and the command-and-control domain became indicators that hunters could search across telemetry. SecondSight hunters used the domain, IP address, and TTP-based signals to identify potentially affected environments and reconstruct attack activity. The value was speed between intelligence, hunt creation, evidence discovery, and action.
Behavioral detection surfaced the anomaly before complete attribution, while IoCs helped confirm attribution and scope affected systems. This also shows how the methods offset investigative costs. The behavioral evidence supplied the context that a package match lacked, and the indicators supplied concrete targets for follow-up searches. In this case, neither a static lookup nor an unexplained anomaly would have provided the same basis for containment.
Why agentic AI creates a detection surface where behavioral methods must lead
Autonomous agents bring the same problem to APIs, tools, and internal systems, where they act at machine speed. The Model Context Protocol, or MCP, is a standardized interface that connects large language models to external tools and data sources. Through those connections, agents can analyze documents, modify infrastructure, generate code, and interact with internal systems at scale. That reach changes the consequences of manipulated instructions. Prompt injection, compromised MCP servers, or hidden instructions in processed content can redirect legitimate capabilities toward harmful ends.
There was no file hash or IP indicator to identify the attack. The detectable deviation lay in the expected tool-call sequence. The agent’s actions, rather than a known malicious artifact, exposed the departure from its assigned work.
In this class of attack, approved channels are not reassuring enough. Commands can run through programs that are approved, actions can use valid credentials, and network calls can reach endpoints they are authorized to use. The order and reach of those actions can show that they are malicious, through tool-call chains, memory access patterns, and reasoning steps. Artifact matching cannot identify a malicious artifact that is absent.
Bollinger et al. identify detection vectors that address this gap. Infrastructure correlation watches for unexpected external connections or replication behavior, while output analysis flags capability concealment or responses inconsistent with the assigned scope. Transcript-based collection looks at reasoning chains and behavioral anomalies that users report. Placing every remote MCP server behind an API gateway creates a single point for authentication, authorization, rate limits, and logging, while short-lived, task-scoped tokens and trimmed context windows limit what a compromised agent can access or exfiltrate.
How hunters combine both methods into a repeatable workflow without drowning in analyst hours
Questions should guide how hunting is organized. Automation provides reach, while analysts decide what is worth investigating and why the evidence is significant. SecondSight describes this division as machines correlating at speed and human curiosity providing direction. The hunter defines the question, applies analytical logic, interprets evidence, and follows unexpected paths. Executing queries is part of that work.
To keep that work focused, teams should keep track of active campaigns and weigh what adversaries want, what they can do, and what opportunities they have in the teams’ own environments before they generate alerts. Each hunt then moves through explicit decisions. Threat intelligence must be relevant, observed behavior must be assessed against known techniques, and environmental exposure must be understood before deciding whether proactive notification is warranted. These decisions constrain both methods. Only some indicators deserve a standing detection, and only some anomalies deserve escalation.
Within that process, IoCs serve confirmation and scoping, while behavioral analytics support early detection and the identification of persistence, privilege escalation, and living-off-the-land activity. Confidence determines the next action. Confirmed hits still require the contextual pivot described earlier, rather than becoming an excuse to stop examining the attack.
Running logic at the network edge allows behavioral models to act on requests in the same point of presence that serves them, without waiting for central aggregation. Edge-based WAF and bot management use this approach, with models that look for patterns across large numbers of requests. Bots may rotate IPs, mimic real browsers, and solve CAPTCHAs, but those adaptations remain open to behavioral analysis. A network spread around the world that handles a large share of internet traffic gets more signals from across its customers, which can improve these models beyond what a point solution on its own can observe.
The supply chain and agent lessons translate into specific coverage requirements. Package environments need behavioral watching for unexpected outbound connections and payload fetching to complement hash-based verification. Agentic workloads need gateway-enforced logging to supply the stream that behavioral detection analyzes. Without telemetry, there is nothing to correlate. The choice between IoCs and behavioral detection is therefore a coverage question, and detection architecture should be designed around the blind spots each method leaves open.