CSPM Tool Evaluation for AWS Azure GCP Deployments
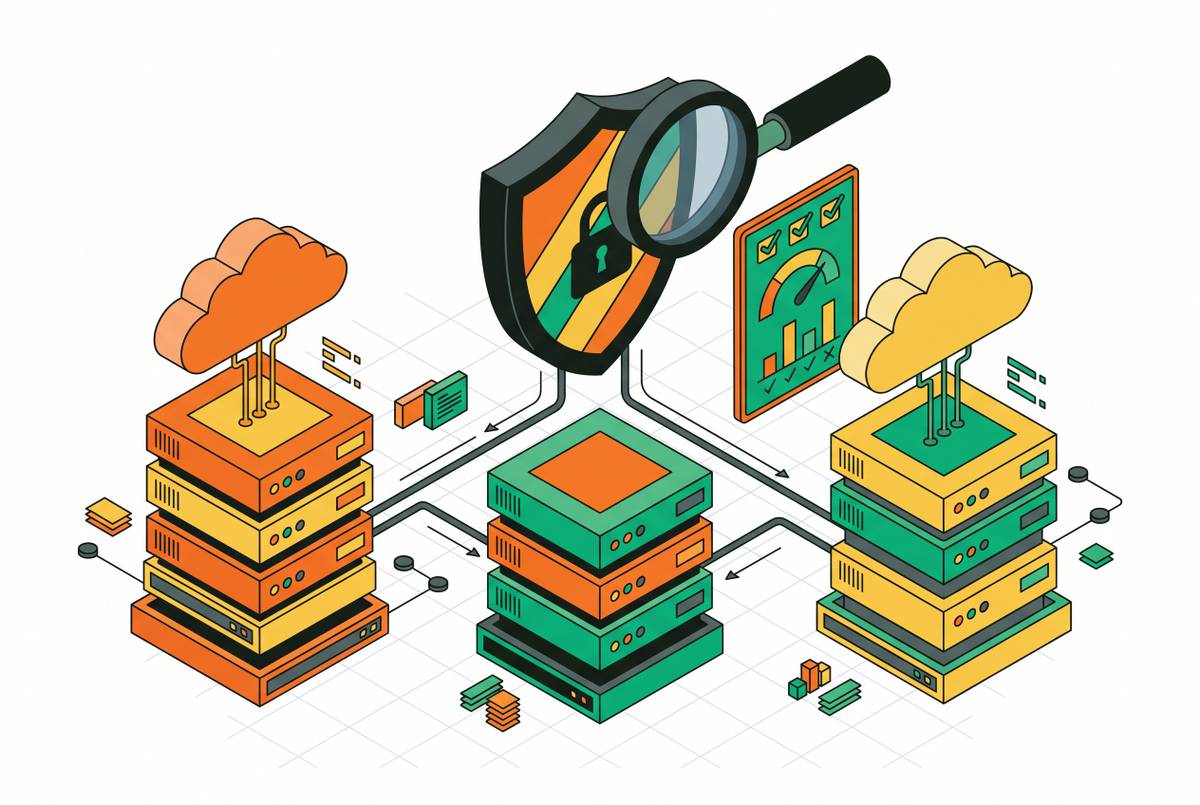
Agentless deployment and coverage depth on your primary cloud matter most for multi-cloud security.
Priya Nanthakumar
Section
16 stories in Zero Trust & SASE.
Agentless deployment and coverage depth on your primary cloud matter most for multi-cloud security.
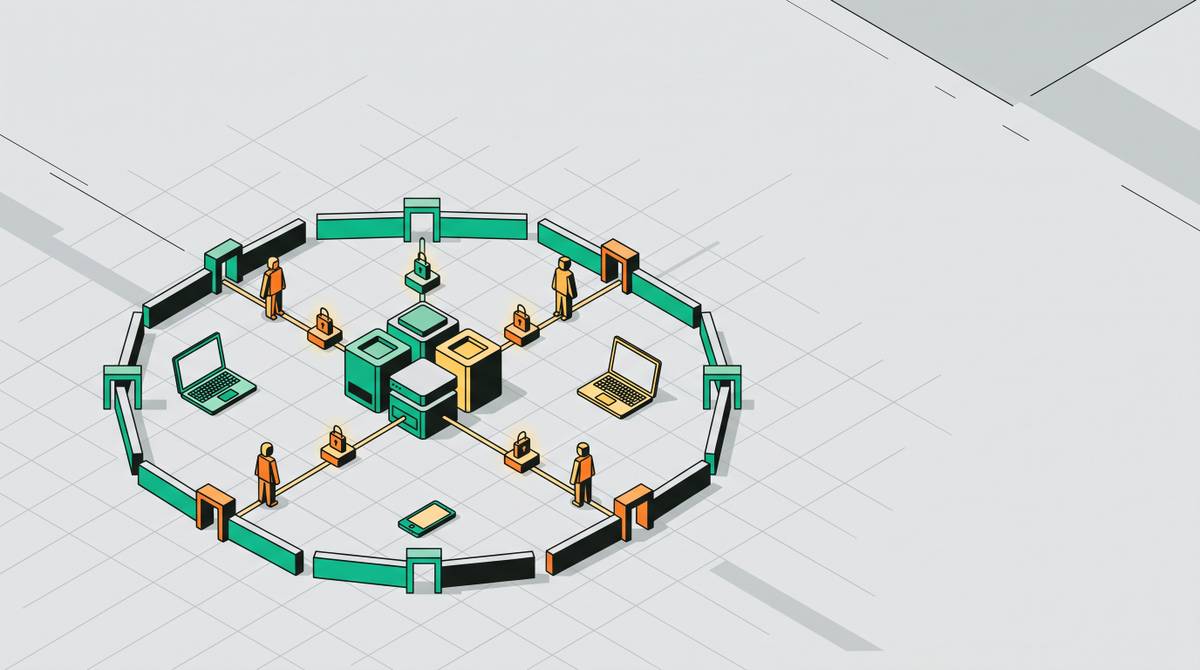
Continuous monitoring of identity, device, and behavior signals, not just login, defines Zero Trust.
Mutual TLS and short-lived credentials replace static secrets with cryptographic proof of identity.
Eliminate standing privilege and scope access to tasks, not vaults.
Continuous monitoring catches SaaS misconfigurations faster than annual audits ever could.
Edge network density and onboarding speed determine whether SASE actually works in production.
Gartner's three separate Magic Quadrants ensure vendors earn recognition on merit, not bundling.
Choosing the wrong connector architecture locks you into years of security tradeoffs.
Encrypted SaaS traffic needs deeper inspection to stop attackers hiding in plain sight.
Compliance mandates force a specific sequence that generic Zero Trust pitches ignore.
Identity becomes the fulcrum—everything else in Zero Trust depends on getting it right.
Verifying the device matters as much as verifying who's using it.
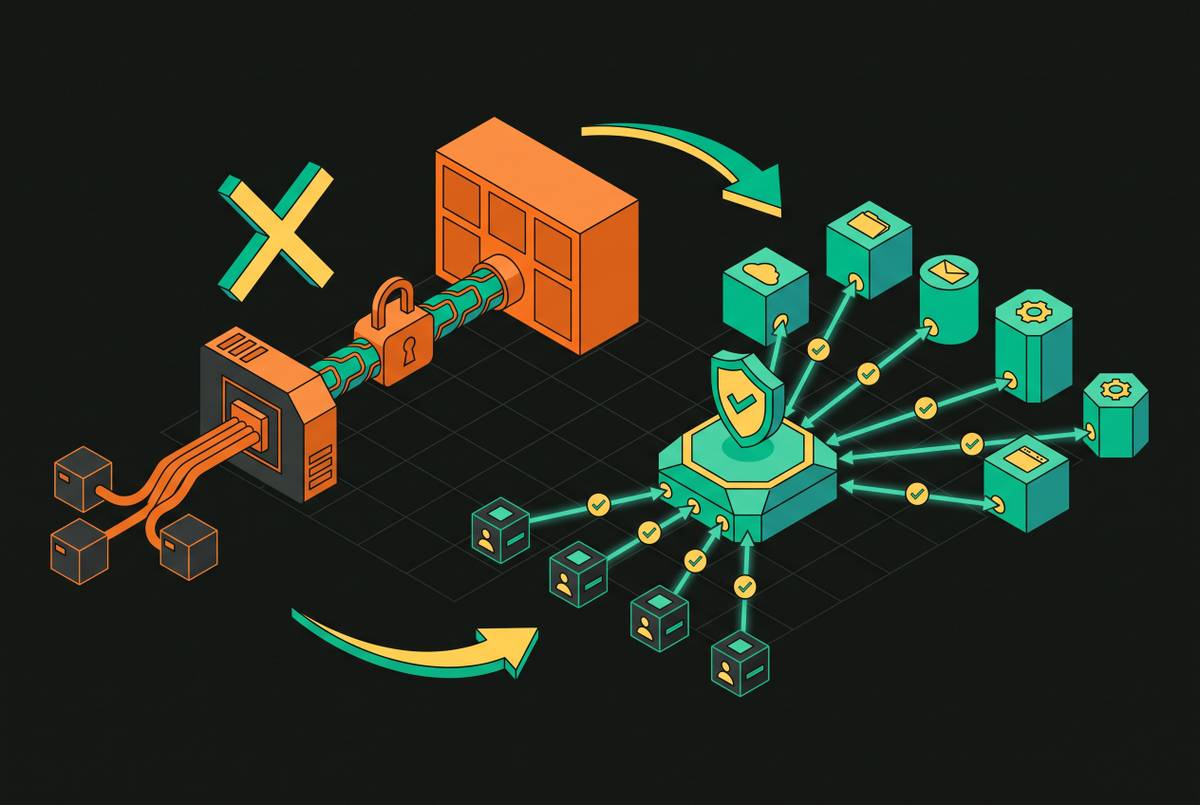
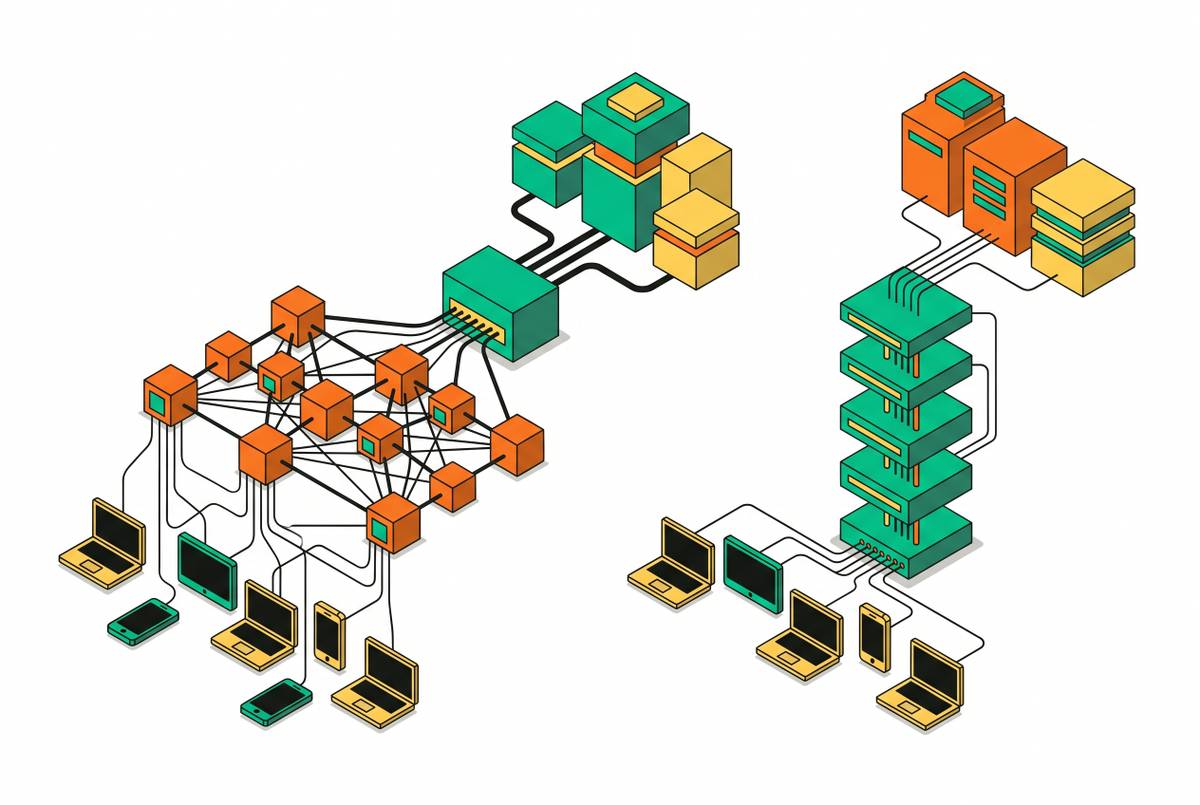
How Zero Trust closes security gaps that VPN architecture leaves wide open.
The choice between SASE and SSE depends on your existing network, not which platform is "better."
Contractors need granular app access, not network-wide VPN trust.
Small teams save $1.76M per incident by adopting Zero Trust, not just surviving breaches.